Nix deployment orchestrator
Panix
Stateless, phase-oriented deployment for Nix flakes, with real-time visibility.
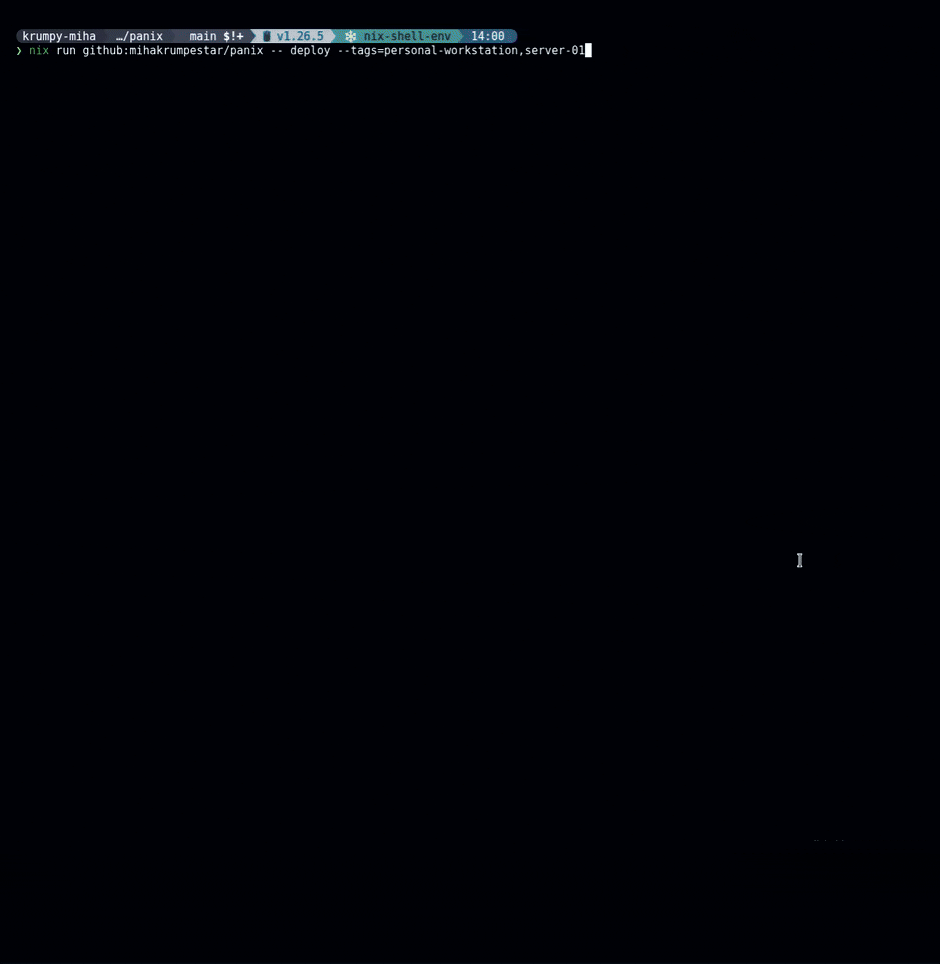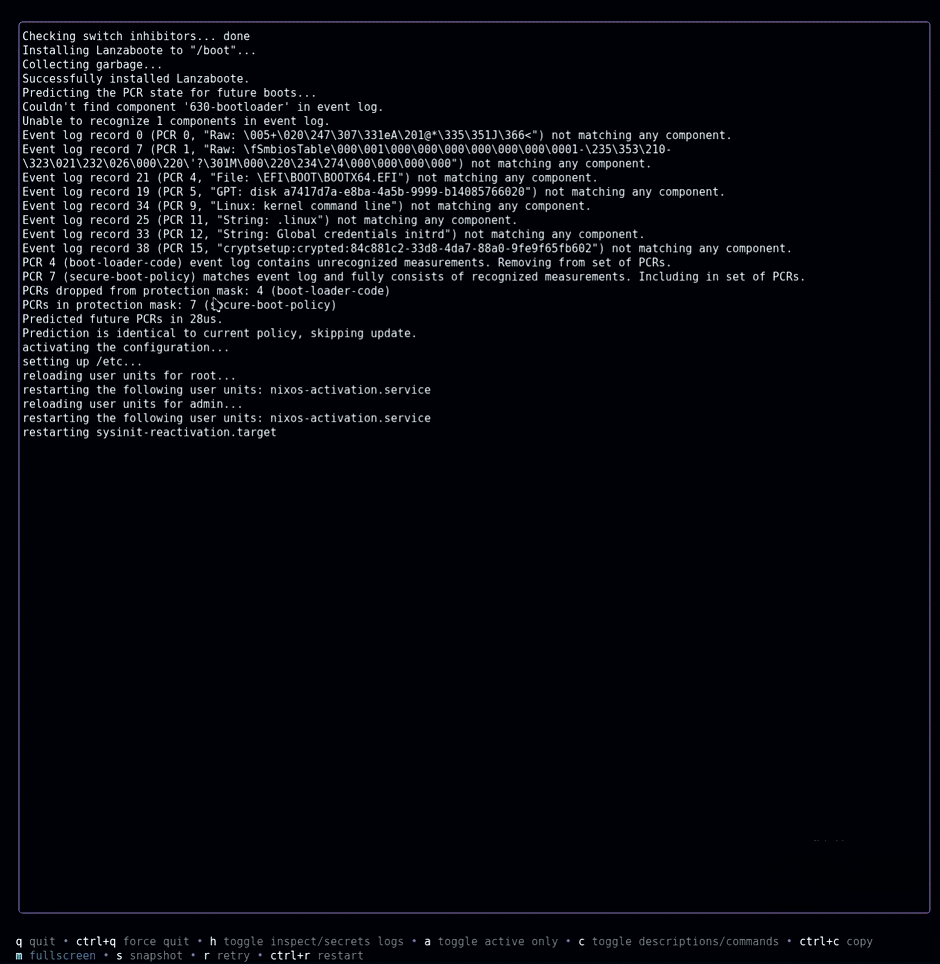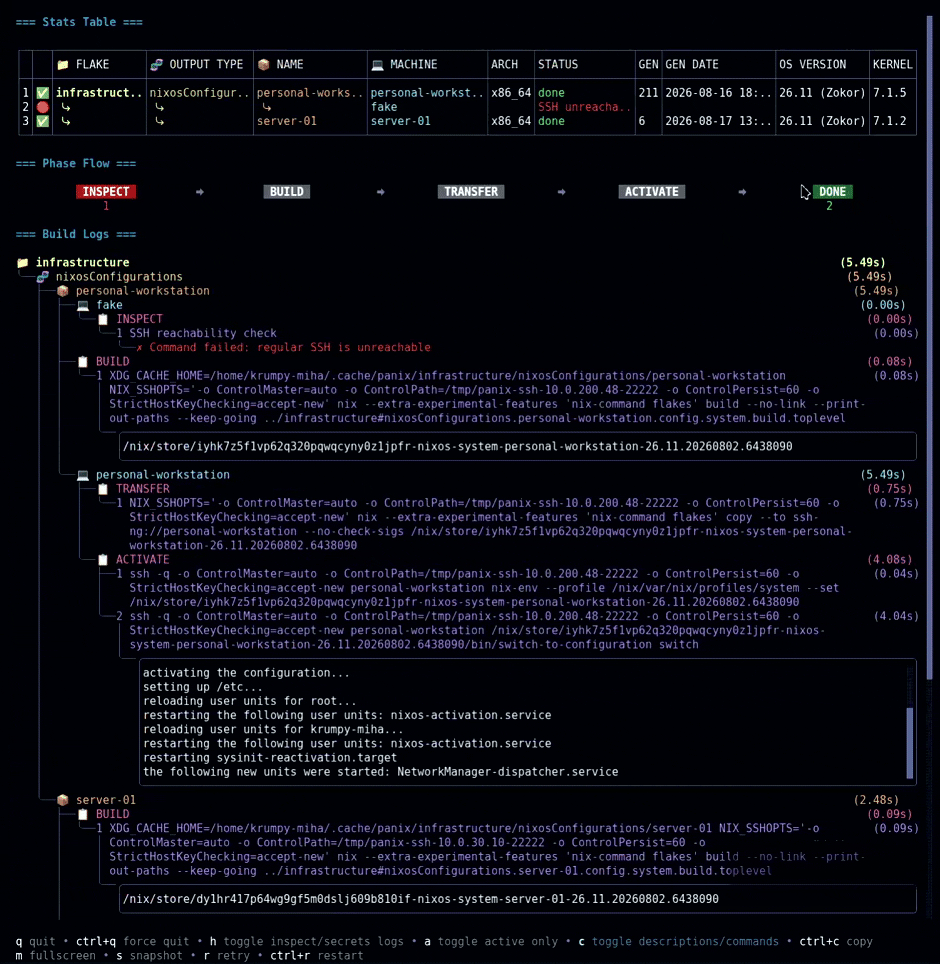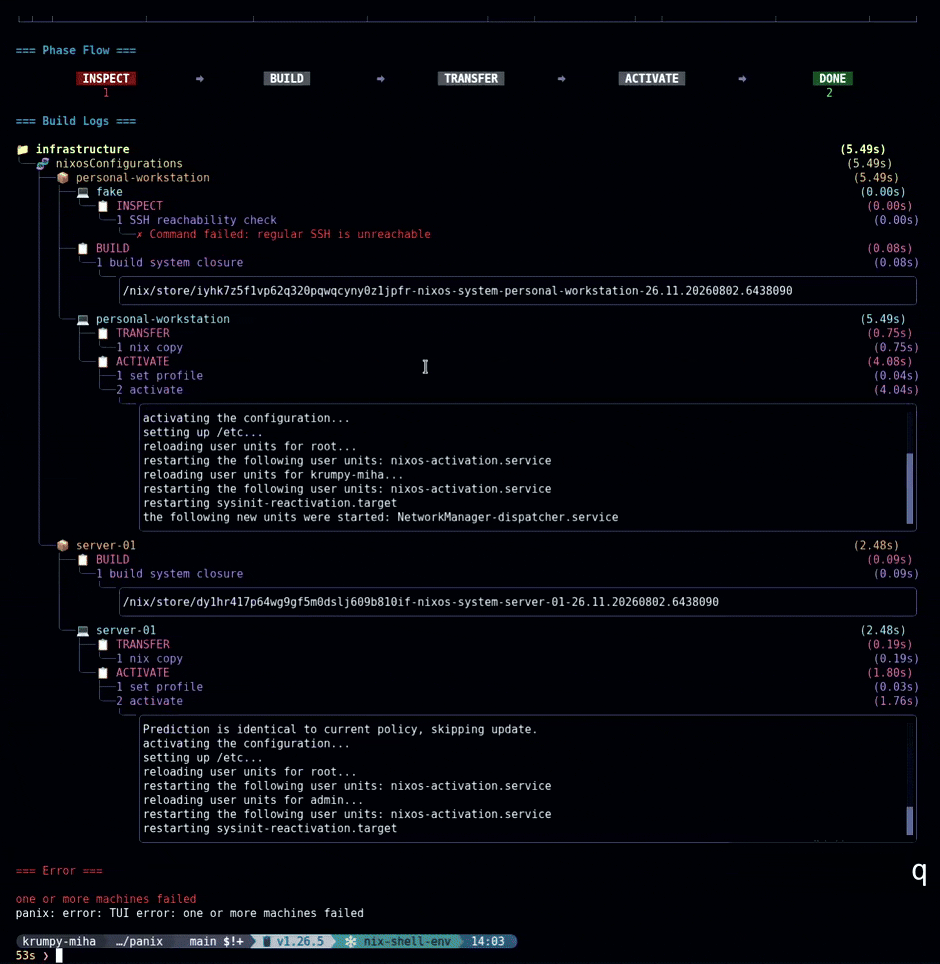
// quickstart
Deploy in two steps
Section titled “Deploy in two steps”- 01 Describe your fleet
One YAML file. No changes to your flake.
panix.yml fleet:flakes:my-infra: # a flake from your repoinstallables:nixosConfigurations: # what to deployweb:machines:web01: # an SSH host - 02 Deploy
Runs straight from the flake, no install step.
sh nix run github:mihakrumpestar/panix -- deploy
// features
What Panix does
Section titled “What Panix does”A phase-oriented pipeline wrapped around your existing flake.
-
Stateless
No state is kept between runs. Every deploy derives from your flake and panix.yml.
How it works -
Real-time TUI
Live progress for every machine and phase. Retry failed phases without restarting.
Keybinds -
Bootstrap bare metal
kexec, disko, and secrets in one command, onto a machine with nothing installed.
Bootstrap guide -
Multi-flake fleets
Machines can come from different flakes and repositories in a single fleet.
Multi-flake -
Tag-based filtering
Deploy a subset of the fleet using tags set at any level of the hierarchy.
Tag filtering -
Any output type
nixosConfigurations, home-manager, and plain packages deploy side by side.
Output types
// comparison
How Panix compares
Section titled “How Panix compares”A comparison between 16 out of 20 NixOS deployment tools.
Every cell links to what verifies it: the feature's own doc section where one exists, otherwise the source file that enumerates the tool's commands or options, since a documentation page cannot state that something is missing. Hover a cell or term for its plain-language meaning. Verified 2026-09-25.
Filter with the row dropdowns, toggle tools with the chips, sort tools with the dropdown above or by clicking a capability name. The filter state is shareable via the URL.
Term glossary
- Yes
- Supported by the tool itself
- No
- Not supported by the tool itself
- Cloud
- Bootstraps by provisioning cloud instances (EC2, GCE, VirtualBox)
- Fleet
- Deploys multiple machines from one config in one run
- Multi-flake
- A fleet can span multiple flakes and repos in one run
- Single
- One machine per invocation
- Per-host
- Each host fetches and applies its own config from a shared source
- TUI
- Interactive terminal UI with live per-machine, per-phase progress
- Web UI
- Browser dashboard for managing devices
- Progress
- Live per-node progress display while deploying
- Status
- Per-host status table (e.g. bento status)
- Metrics
- Prometheus exporter and desktop notifiers
- CLI output
- The deployment command's own output; nothing else
- None
- No built-in support in the tool itself
- On-target
- You run it on the machine being changed
- On-demand
- A check command exists, but it is not run automatically after deploy
- Auto
- Rolls back automatically on activation failure
- Magic
- Rolls back when the target loses contact with the deployment source after switching
- Manual
- Explicit rollback command only
- Push
- Deploys from your machine to targets over SSH
- Pull
- Targets fetch updates themselves on a schedule
- Controller
- A central server actively orchestrates the devices, which connect to it
- Stateless
- No state kept between runs; everything is re-derived
- Stateful
- Keeps a state database or vars that later deploys depend on
- Unchanged
- Your existing configs are consumed as-is; nothing is wired in
- Adapter
- The tool needs a module, output, or import wired into your flake or configs
- Rewrite
- Your configs must be rebuilt around the tool's own format
- Plaintext
- Secrets are transferred to the machine as-is, outside the Nix store; the tool itself does no decryption
- Deployment keys
- Secrets are pushed as key files through deployment.keys (the default /run/keys is in-memory; destDir can target persistent paths)
- Activation
- Encrypted at rest; the machine holds the key and decrypts locally at activation
- Pre-transfer
- Encrypted at rest; the control host decrypts before transfer, so targets never hold a key
- Install-phase
- Secrets are only handled during the install phase